XDR monitoring and security for your entire estate.
Sentinel NX is an XDR platform available as two products, Sentinel NX Monitoring and Sentinel NX Security, or integrated in Sentinel NX Security Suite.

Sentinel NX Security Suite
by NX Informatics
- Host availability & uptime
- CPU, memory, disk & network
- Problems & acknowledgements
- Geographic site map
- Alerts, firewall & FIM
- EDR & malware detections
- Vulnerabilities & hardening
- Compliance & MITRE ATT&CK
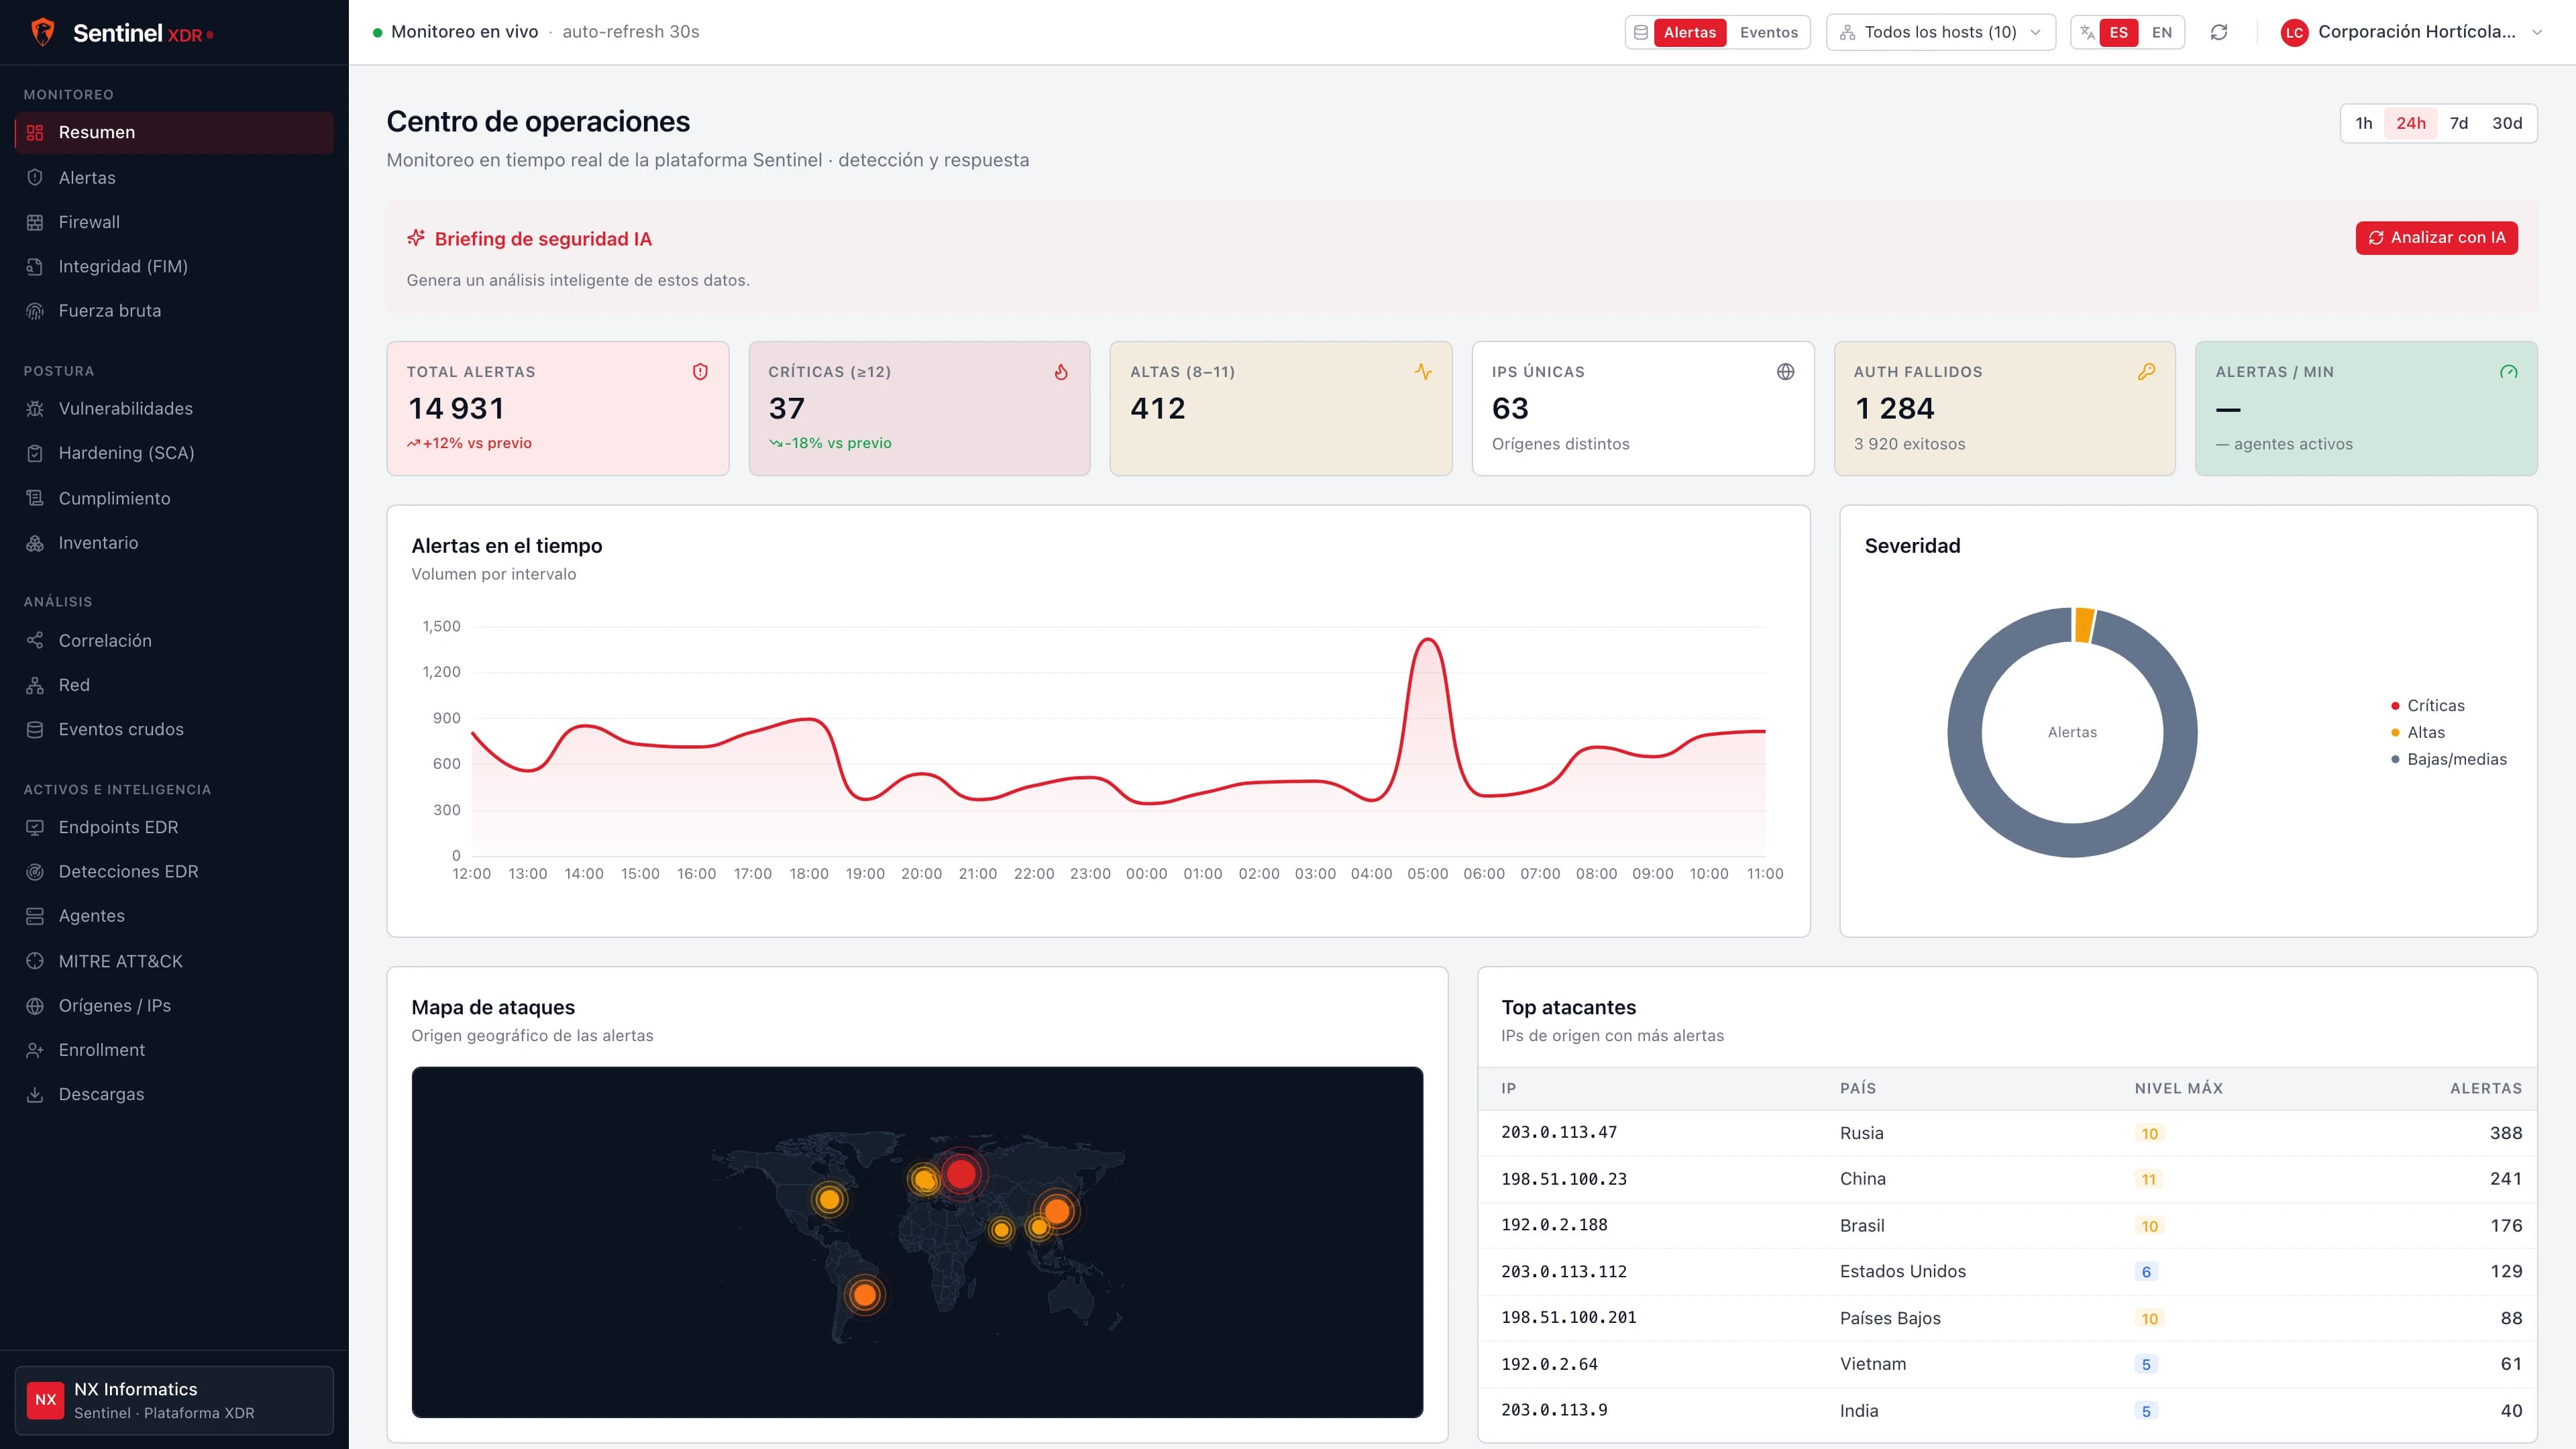
Your security operations at a glance
Alerts over time, severity, attack origins and top attackers for every host, live.
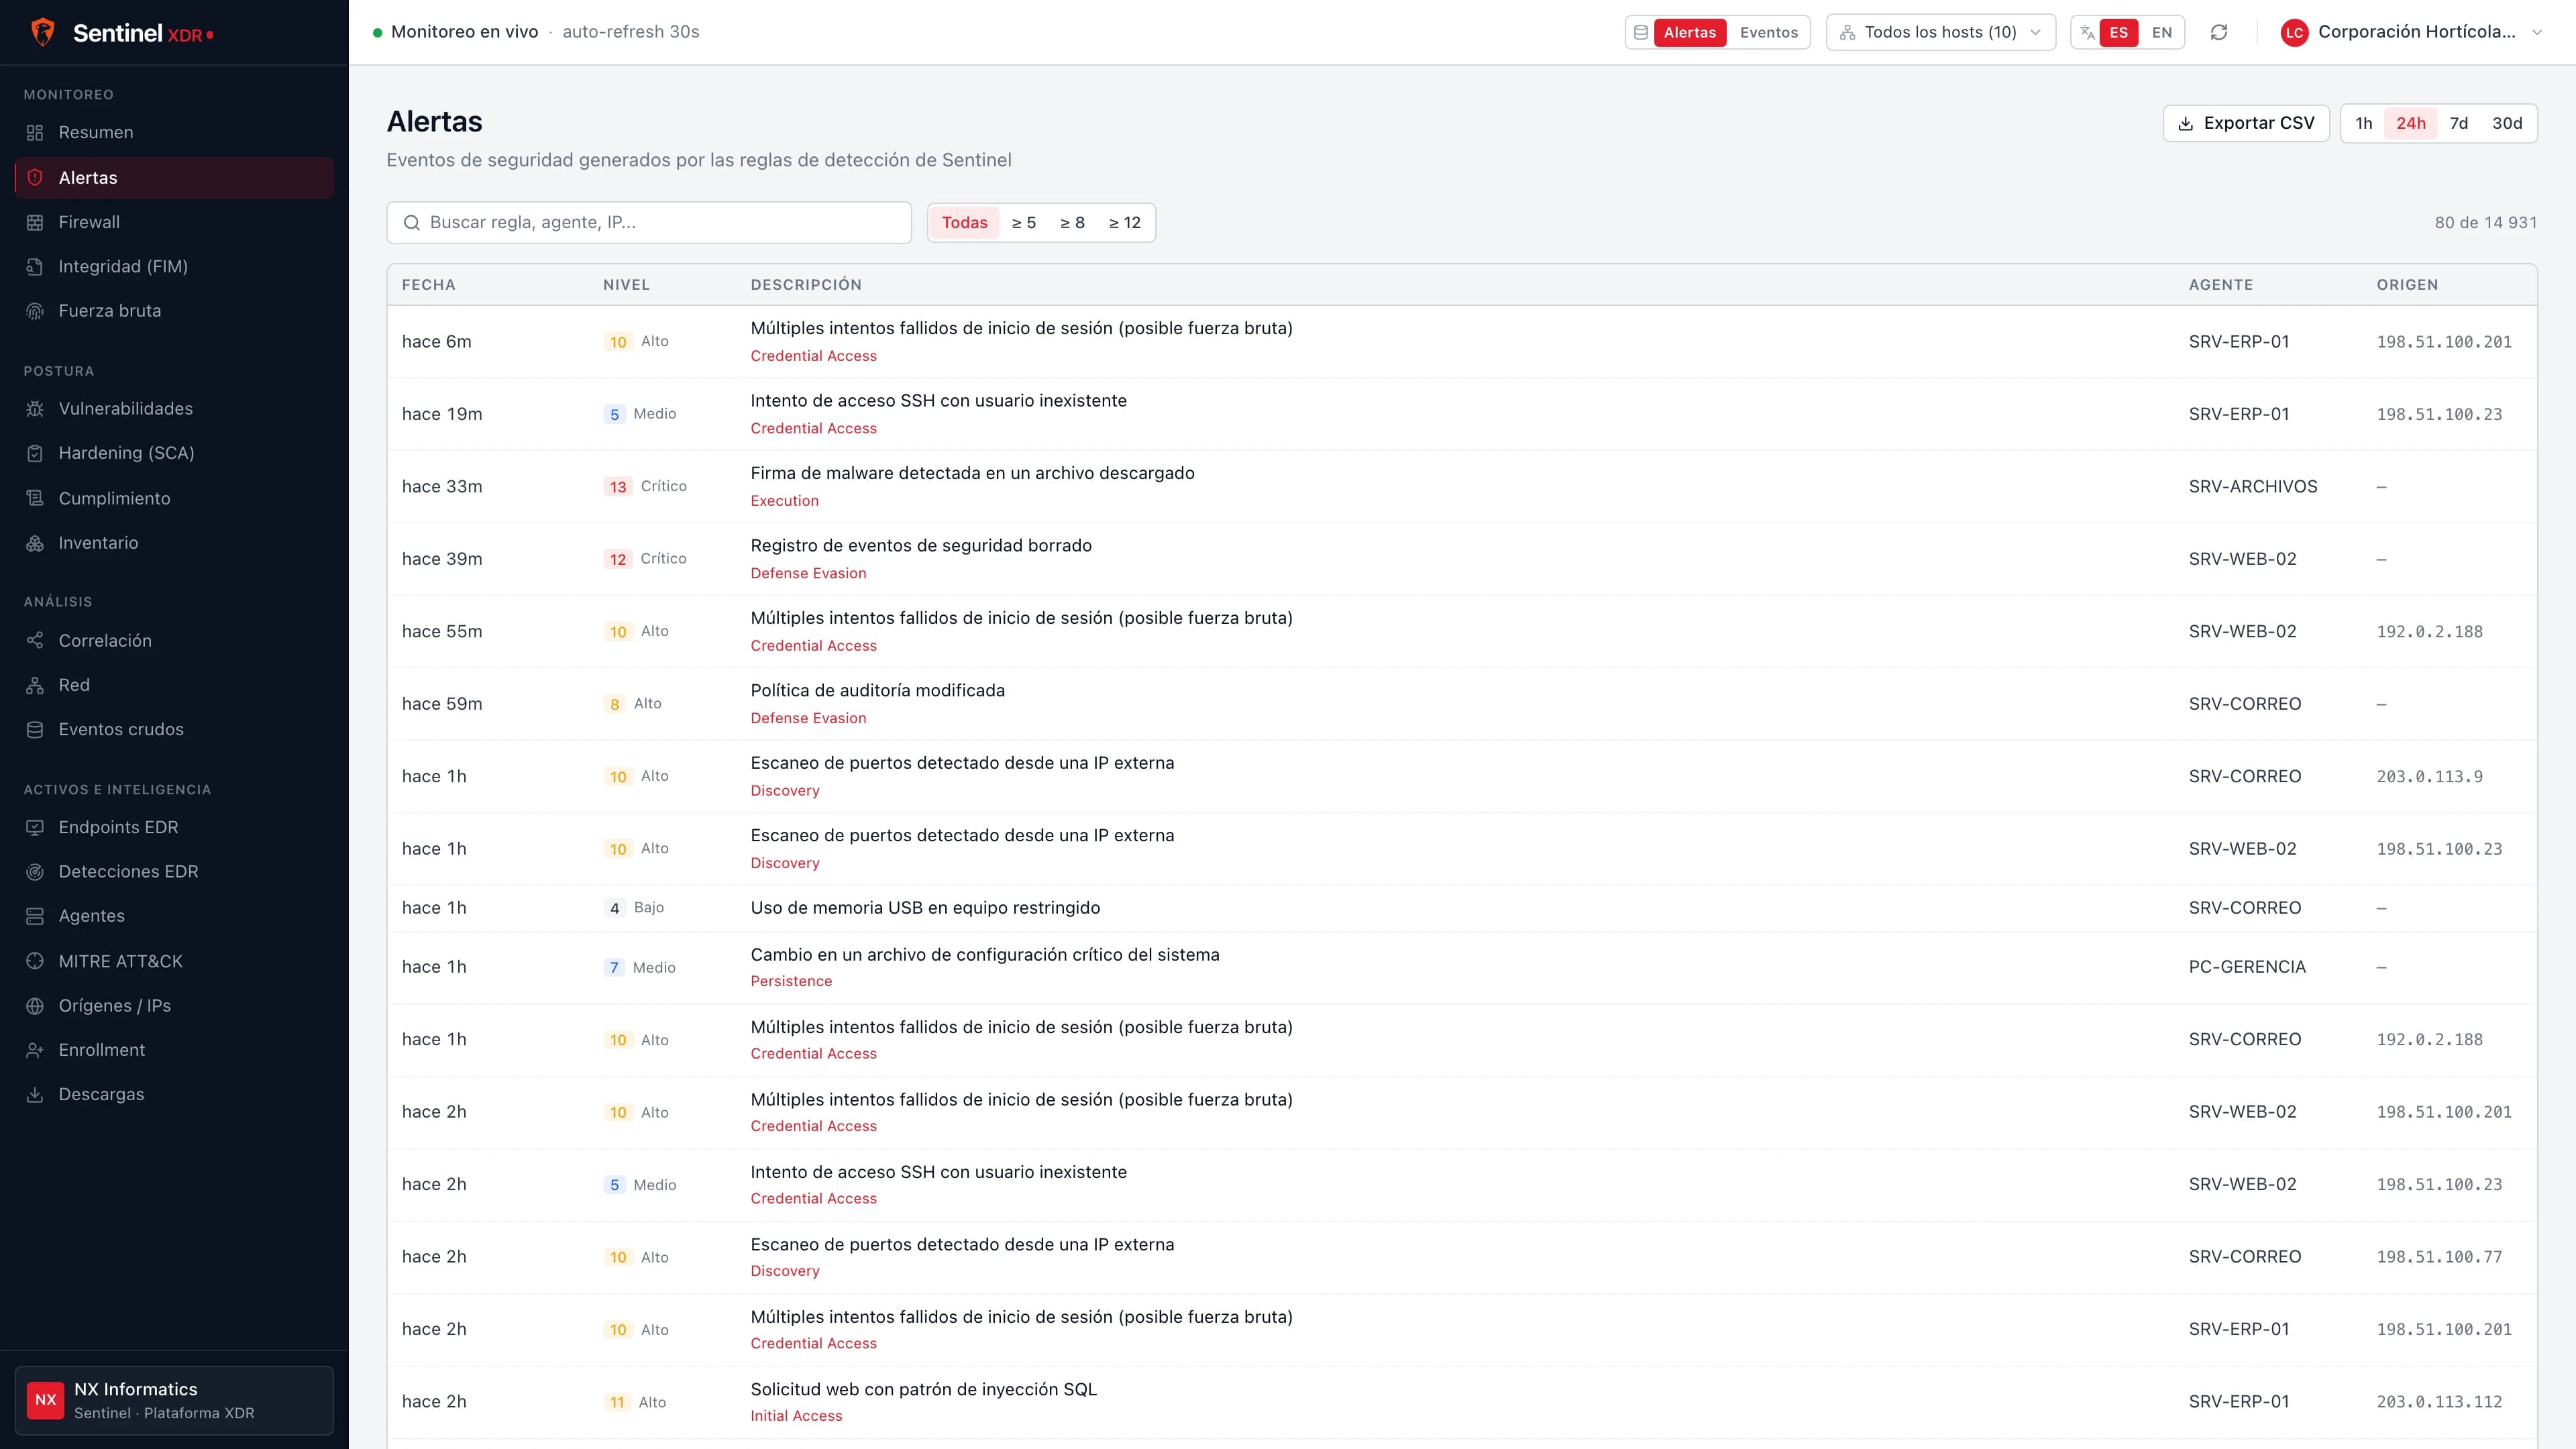
Every alert, ready to act on
Search, filter and export alerts by severity, MITRE ATT&CK tactic, host and source IP.
Available editions.
Monitoring, security or both in a single suite.
Sentinel NX Monitoring
Every host. Every site. In real time.
Monitoring for servers, networks and sites: availability, performance and incidents, from the site map down to every disk.
- Host availability & uptime
- CPU, memory, disk and network per host
- Problem management: acknowledge, comment, close
- Geographic map of sites
- Top resource consumers with 24h trends
- Automatic agent registration
Sentinel NX Security
Your entire estate, in a single panel.
Extended detection and response: alerts, endpoints, vulnerabilities and compliance across the organization, with notifications in the portal and Microsoft Teams.
- Security alerts, firewall, FIM & brute-force detection
- EDR endpoints & malware detections
- Vulnerabilities (CVE/CVSS) & hardening (SCA)
- Compliance posture: PCI DSS, NIST 800-53, HIPAA, GDPR
- MITRE ATT&CK mapping & attack origins
- AI-assisted analysis & Microsoft Teams alerts
Sentinel NX Security Suite
Monitoring and security, unified.
Both products in one platform, with availability and threat visibility for every host in a single deployment.
- Everything in Sentinel NX Monitoring
- Everything in Sentinel NX Security
- One enrollment for security and monitoring
- All-in-one Windows installer
- Multi-tenant with roles & audit trail
- Spanish & English interface
Alerts mapped to PCI DSS, NIST 800-53, HIPAA, GDPR and other framework controls.
From detection to response.
Deploy agents
Agent installation on Windows, Debian/Ubuntu and RHEL-family hosts with an encrypted, signed enrollment file.
Monitor & detect
Availability, performance, events and threats are analyzed continuously.
Alert the team
Prioritized alerts reach the panel and Microsoft Teams in real time.
Respond & report
AI-assisted analysis, problem management and compliance reporting.
Detections mapped to MITRE ATT&CK tactics, with the attack-chain stage shown on every alert.
Complete visibility across your infrastructure.
Request a Sentinel NX demo with our security team.
Access restricted to your organization.
Every query is scoped on the server to the organization's data. Out-of-scope access attempts are blocked and logged.
- Instantly revocable sessions, closed after 4 hours of inactivity
- Account lockout after failed sign-in attempts
- Device enrollment with an encrypted, signed file
- Audit log of sign-ins, changes and denied access
- Internal credentials never exposed to the browser
Real-time alerts for your IT team.
Critical alerts are delivered to Microsoft Teams, where the team already works.
Microsoft Teams
Alert cards in one or more channels, deduplicated over 24 hours.
Malware detection
Immediate notification when a new threat is detected on a device.
Unprotected devices
Agents not reporting, disabled modules or outdated signatures.
High risk
Notification when a device's risk exceeds the threshold, and when it returns to normal.
AI-assisted analysis
Alert explanations, attacker profiling and an executive summary.
Windows and Linux
Agents for Windows and Linux on x86_64 and ARM64.
Sentinel NX FAQ.
Answers about scope, services and how we work.
More from ATSC
Complementary platforms


More services